Investigate What Others Can't
Six specialized forensics disciplines — email trails, blockchain transactions, steganographic payloads, drone telemetry, IoT ecosystems, and penetration testing — taught with the rigor and real-world framing that actual casework demands.
"Every lesson I write starts with the same question: if this went to court tomorrow, would the investigator be ready?"
— PROF. PETER OLU. OLAYIWOLA, Ph.D.
What you'll learn
What you'll be able to do
- Conduct end-to-end email forensics investigations, tracing spoofed headers, analyzing SMTP logs, and recovering deleted correspondence as court-admissible evidence.
- Trace and attribute cryptocurrency transactions across Bitcoin and Ethereum blockchains using chain-analysis tools to follow illicit fund flows.
- Detect, extract, and decode data concealed via steganography in image, audio, and video files using industry-standard steg-analysis toolkits.
- Perform forensic acquisition and analysis of drone flight logs, GPS telemetry, and onboard storage to reconstruct flight events and operator identity.
- Collect and analyze evidence from IoT ecosystems — smart home hubs, wearables, and embedded firmware — while preserving chain of custody.
- Execute structured ethical hacking and penetration testing engagements, documenting findings in professional reports that meet legal and compliance standards.
How it works
A school that adapts to you
This isn't a set of static videos. Every lesson is generated live and tuned to where you actually are.
We learn your level
A quick placement check tailors your starting point so you're never bored or lost.
Lessons adapt as you go
Each lesson is written for your pace and your goal, adjusting as your skills grow.
Your AI coach keeps you moving
Checkpoints, feedback, and gentle nudges turn progress into a real result.
The curriculum
What's inside your school
0 modules · 0 lessons
Email Forensics
Covers end-to-end investigation of email evidence, from header analysis and SMTP log tracing to recovering deleted messages and packaging findings as court-admissible evidence.
- 1.1Email Architecture and the Investigator's MindsetIncluded
- 1.2Header Analysis and Spoofing DetectionIncluded
- 1.3SMTP Log Acquisition and AnalysisIncluded
- 1.4Recovering Deleted and Encrypted EmailIncluded
- 1.5Building Court-Admissible Email Evidence PackagesIncluded
Cryptocurrency Forensics
Trains investigators to trace and attribute illicit fund flows across Bitcoin and Ethereum blockchains using professional chain-analysis platforms and on-chain evidence techniques.
- 2.1Blockchain Fundamentals for InvestigatorsIncluded
- 2.2Tracing Bitcoin Transactions and Clustering WalletsIncluded
- 2.3Ethereum and Smart Contract InvestigationIncluded
- 2.4Using Chain-Analysis PlatformsIncluded
- 2.5Mixing Services, Privacy Coins, and Attribution StrategiesIncluded
Steganography Forensics
Equips investigators to detect, extract, and decode data hidden in image, audio, and video files using steg-detection algorithms and industry-standard toolkits.
- 3.1Steganography Concepts and Threat LandscapeIncluded
- 3.2Image Steganography Detection and ExtractionIncluded
- 3.3Audio and Video Steganography AnalysisIncluded
- 3.4Document and Network SteganographyIncluded
- 3.5Documenting Steg Evidence for Legal ProceedingsIncluded
Drone Forensics
Covers the full forensic workflow for unmanned aerial vehicles — from safe acquisition of onboard storage and flight logs to GPS telemetry reconstruction and operator attribution.
- 4.1Drone Ecosystem and Evidence SourcesIncluded
- 4.2Forensic Acquisition of Drone Storage and MemoryIncluded
- 4.3Flight Log and GPS Telemetry AnalysisIncluded
- 4.4Operator Identification and Mobile App ForensicsIncluded
- 4.5Reporting Drone Incidents for Regulatory and Legal UseIncluded
IoT Forensics
Trains investigators to acquire and analyze evidence from heterogeneous IoT ecosystems — including smart home hubs, wearables, and embedded firmware — while maintaining chain of custody.
- 5.1IoT Architecture and Forensic Attack SurfaceIncluded
- 5.2Forensic Acquisition of IoT Devices and FirmwareIncluded
- 5.3Smart Home Hub and Wearable Evidence AnalysisIncluded
- 5.4Cloud and API Evidence Collection for IoT CasesIncluded
- 5.5Chain of Custody and Reporting in IoT InvestigationsIncluded
Ethical Hacking and Penetration Testing
Guides investigators through structured penetration testing engagements — scoping, execution, and professional reporting — fully aligned with legal requirements and compliance frameworks.
- 6.1Legal Foundations and Rules of EngagementIncluded
- 6.2Reconnaissance and OSINT for Penetration TestersIncluded
- 6.3Exploitation Techniques and ToolingIncluded
- 6.4Post-Exploitation, Pivoting, and Evidence HandlingIncluded
- 6.5Writing Professional Penetration Testing ReportsIncluded
Who it's for
Is this you?
Corporate Incident Responders
When a breach hits the boardroom agenda, they need the specialized acquisition and reporting skills to investigate IoT, email, and endpoint evidence that holds up under legal scrutiny.
Law Enforcement Analysts
They handle complex financial crime and cyber cases and need court-ready methodology for tracing cryptocurrency, parsing drone telemetry, and packaging digital evidence for prosecution.
Digital Forensics Consultants
Independent practitioners expanding their service offering need command of high-demand specializations — blockchain tracing, steg analysis, IoT acquisition — to win more complex engagements.
Penetration Testers Moving into Forensics
They already know how to get in — now they need to understand how forensic investigators reconstruct what happened, and how to write findings that satisfy legal and compliance standards.
Cybersecurity Team Leads
Responsible for building a team's investigative capability, they need deep fluency across emerging evidence domains so they can triage, delegate, and QA specialized casework with confidence.
Expert Witness Candidates
Experienced practitioners seeking to qualify as forensic expert witnesses need the precise, defensible methodology and documentation discipline that cross-examination demands.
Questions
Frequently asked
Your teacher
A note from your teacher
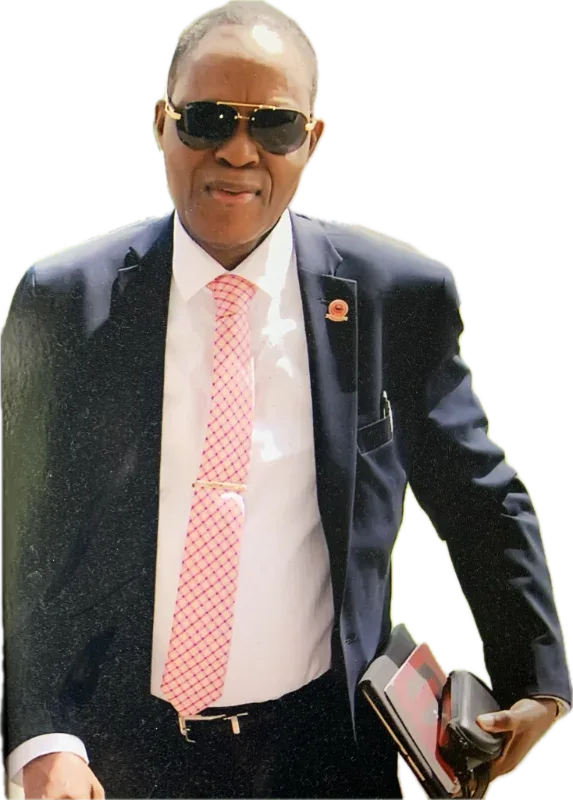
PROF. PETER OLU. OLAYIWOLA, Ph.D.
If you're reading this, you've probably already sat through the introductory forensics training. You know what a forensic image is. You know why you never write to original media. You understand chain of custody in principle. And yet — when the case involves a wallet address laundering funds through a mixing service, or a suspect's DJI drone, or a payload hidden inside a JPEG attachment — you've felt the gap between what you were trained to do and what the case actually demands.
That gap is exactly what this program is designed to close.
I built Advanced Digital Forensics around the six specializations that keep surfacing in the hardest cases — the ones that get escalated, that end up in federal court, that make or break a corporate investigation. Email fraud with spoofed headers and deleted correspondence. Cryptocurrency flows that bounce through Ethereum smart contracts and privacy coins before they hit an exchange. Steganographic payloads hidden in audio files that would sail past a standard review. Drone incidents where the onboard storage and the operator's phone tell completely different stories. IoT ecosystems where the evidence is split between a wearable, a cloud API, and firmware nobody documented. Penetration test engagements that need reporting rigorous enough to satisfy a compliance auditor and a general counsel simultaneously.
Each module is structured the way I think about an actual investigation: identify the evidence surface, acquire it in a forensically sound manner, analyze it with discipline, and document everything so it survives scrutiny. I don't pad lessons with theory for theory's sake. If a concept is in here, it's because it shows up in real casework and you need to be able to execute it — not just describe it.
One thing I want to be direct about: this program won't hand you a checklist that works on every case forever. Blockchains fork. Drone manufacturers update their log formats. IoT vendors move evidence to new cloud endpoints. What I'm teaching you is a methodology rigorous enough to adapt — so when the technology shifts, your investigative instincts don't fail you. The professionals who stay valuable in this field are the ones who understand the principles deeply enough to work through novel problems. That's who I'm teaching to.
If you're ready to build the kind of specialized, documentable expertise that gets you called in when the case gets hard, let's get to work.
— PROF. PETER OLU. OLAYIWOLA, Ph.D.
Start your journey today
Get instant access — learn at your own pace with an AI coach in your corner.
$125/mo
Recurring billing · cancel anytime
Secure checkout · Instant access
- 6 modules, 30 lessons
- AI-adaptive lessons tuned to your level
- Quizzes & checkpoints to lock in progress
- Your own AI learning coach
- Learn on any device, at your pace
- Full access for as long as you're subscribed