Think like an attacker. Defend like an expert.
CyberShield Academy takes IT and security professionals beyond certification-level theory — into hands-on penetration testing, digital forensics, malware analysis, and enterprise defense architecture used by elite practitioners in the field.
"You can't build defenses that hold until you truly understand how they break — so we start with the attacker, and we don't cut corners."
— PROF. PETER OLU. OLAYIWOLA, Ph.D.
What you'll learn
What you'll be able to do
- Identify and exploit common attack vectors — including SQL injection, XSS, and man-in-the-middle attacks — to understand and close real vulnerabilities
- Conduct professional-grade penetration tests on networks and web applications using tools like Metasploit, Burp Suite, and Wireshark
- Investigate cybercrime incidents using digital forensics methodologies, including evidence preservation, chain-of-custody, and log analysis
- Design and implement layered network defense architectures including firewalls, IDS/IPS systems, and zero-trust frameworks
- Analyze and respond to live malware samples, reverse-engineer attack code, and produce incident response reports
- Understand the legal landscape of cybercrime — including CFAA, GDPR, and international frameworks — and apply compliance best practices to real-world scenarios
How it works
A school that adapts to you
This isn't a set of static videos. Every lesson is generated live and tuned to where you actually are.
We learn your level
A quick placement check tailors your starting point so you're never bored or lost.
Lessons adapt as you go
Each lesson is written for your pace and your goal, adjusting as your skills grow.
Your AI coach keeps you moving
Checkpoints, feedback, and gentle nudges turn progress into a real result.
The curriculum
What's inside your school
0 modules · 0 lessons
Advanced Attack Vectors and Adversary Thinking
Dissects the most dangerous attack techniques — SQL injection, XSS, MitM, and beyond — so students can identify and exploit vulnerabilities the way real attackers do.
- 1.1Anatomy of an Attack: Threat Modeling and the Attacker MindsetIncluded
- 1.2SQL Injection In Depth: Detection, Exploitation, and RemediationIncluded
- 1.3Cross-Site Scripting (XSS): Reflected, Stored, and DOM-Based AttacksIncluded
- 1.4Man-in-the-Middle Attacks: Interception, SSL Stripping, and ARP PoisoningIncluded
- 1.5Social Engineering and Phishing: Human-Layer Attack VectorsIncluded
Professional Penetration Testing
Builds a structured, methodology-driven penetration testing workflow using industry-standard tools across network and web application targets.
- 2.1Penetration Testing Methodology: Scoping, Rules of Engagement, and ReportingIncluded
- 2.2Reconnaissance and Enumeration: OSINT, Nmap, and FootprintingIncluded
- 2.3Exploitation with Metasploit: Modules, Payloads, and Post-ExploitationIncluded
- 2.4Web Application Penetration Testing with Burp SuiteIncluded
- 2.5Network Traffic Analysis and Packet Inspection with WiresharkIncluded
Malware Analysis and Incident Response
Trains students to safely analyze live malware samples, reverse-engineer attack code, and produce professional incident response documentation.
- 3.1Setting Up a Safe Malware Analysis Lab: Sandboxes and IsolationIncluded
- 3.2Static Malware Analysis: File Hashing, Strings, and DisassemblyIncluded
- 3.3Dynamic Malware Analysis: Behavioral Monitoring and Network CallbacksIncluded
- 3.4Reverse Engineering Attack Code: Decompilers and Control Flow AnalysisIncluded
- 3.5Incident Response: Containment, Eradication, and Professional ReportingIncluded
Digital Forensics and Cybercrime Investigation
Covers the full digital forensics pipeline — evidence acquisition, chain-of-custody, log analysis, and court-ready documentation — for professional cybercrime investigations.
- 4.1Foundations of Digital Forensics: Evidence Integrity and Chain of CustodyIncluded
- 4.2Disk and Memory Forensics: Imaging, Acquisition, and Artifact RecoveryIncluded
- 4.3Log Analysis and Timeline ReconstructionIncluded
- 4.4Network Forensics: Tracing Intrusions Through Packet and Flow DataIncluded
- 4.5Documenting and Presenting Forensic Findings for Legal ProceedingsIncluded
Layered Network Defense Architecture
Teaches students to design and implement enterprise-grade defensive architectures — from perimeter firewalls to zero-trust micro-segmentation — that stop modern threats.
- 5.1Defense-in-Depth: Principles of Layered Security ArchitectureIncluded
- 5.2Firewall Configuration and Rule Management for Enterprise NetworksIncluded
- 5.3Intrusion Detection and Prevention Systems: Deployment and TuningIncluded
- 5.4Zero-Trust Architecture: Identity Verification, Micro-Segmentation, and Least PrivilegeIncluded
- 5.5Security Monitoring and SIEM Integration for Continuous DefenseIncluded
Cybercrime Law, Compliance, and Ethical Practice
Grounds every technical skill in the legal frameworks — CFAA, GDPR, and international law — and compliance practices that govern professional cybersecurity work.
- 6.1The Computer Fraud and Abuse Act (CFAA): Boundaries of Legal Security TestingIncluded
- 6.2GDPR and US Privacy Law: Data Protection Obligations for Security TeamsIncluded
- 6.3International Cybercrime Frameworks: Budapest Convention and Cross-Border JurisdictionIncluded
- 6.4Compliance Frameworks in Practice: NIST CSF, ISO 27001, and SOC 2Included
- 6.5Ethics, Responsible Disclosure, and Building a Professional Security PracticeIncluded
Who it's for
Is this you?
Network Administrators
Ready to move from managing infrastructure to actively defending it — with the penetration testing and IDS/IPS skills to back it up.
Security Analysts
Handles alerts and incidents daily and needs the malware analysis, forensics, and SIEM-depth to investigate faster and report with precision.
Aspiring Pen Testers
Has the technical foundation and is ready to execute professional-grade engagements with Metasploit, Burp Suite, and structured reporting methodology.
IT Professionals Upskilling
Strong in systems or networking and wants to pivot into a dedicated security role with hands-on, portfolio-ready skills.
Compliance & Risk Managers
Needs to connect technical controls to NIST CSF, ISO 27001, SOC 2, and GDPR obligations — and finally speak the same language as the security team.
Cybercrime Investigators
Works on or alongside law enforcement or legal teams and needs rigorous digital forensics skills — from chain-of-custody to court-ready documentation.
Questions
Frequently asked
Your teacher
A note from your teacher
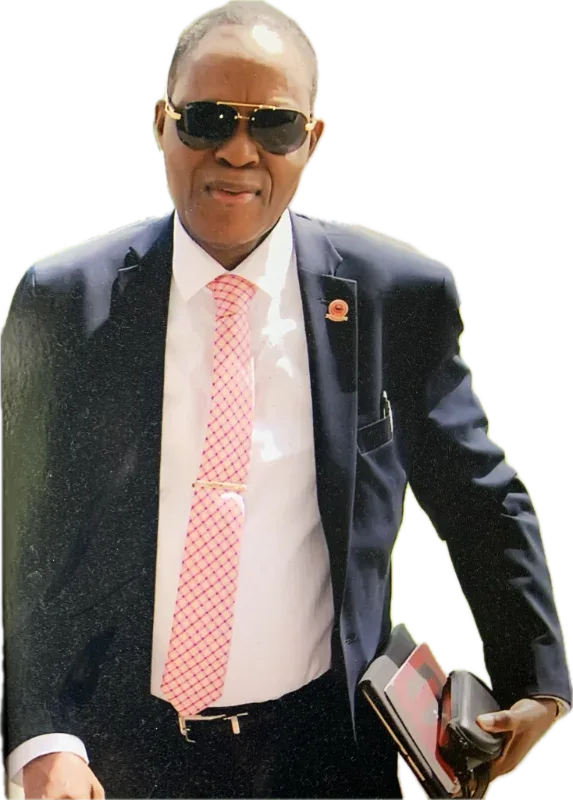
PROF. PETER OLU. OLAYIWOLA, Ph.D.
If you've been working in IT or security for a while, you already know the frustration. You've passed the foundational exams. You understand the concepts. But when a real incident lands — a breach, a suspicious binary, an intrusion you need to trace back to its source — there's a gap between what certifications taught you and what the situation actually demands. That gap is what CyberShield Academy was built to close.
Security work at a serious level requires you to think from both sides of the wire. You need to understand how attackers operate — not in abstract terms, but at the level of SQL injection payloads, XSS vectors, ARP poisoning, and social engineering pretexts — because you cannot effectively defend what you don't understand how to break. That's why this curriculum begins with adversary thinking and moves through hands-on exploitation before it ever asks you to think about defense. Understanding the offense is the prerequisite for building defenses that actually hold.
What I've tried to build here is the curriculum I wish had existed when I was moving from competent generalist to specialist. Every module is structured around what professionals are actually asked to do: scope and execute a penetration test, stand up a malware analysis lab, conduct forensic acquisition without contaminating evidence, tune an IDS without drowning in false positives, and write findings that survive legal scrutiny. The tools are real — Metasploit, Burp Suite, Wireshark, forensic imaging tools, decompilers. The methodologies are the ones the field actually uses.
The legal and compliance module exists because I've seen technically excellent security professionals make career-ending mistakes by operating outside clearly defined boundaries. The CFAA, GDPR, NIST CSF, ISO 27001 — these aren't bureaucratic overhead. They're the framework that separates a professional security practice from liability. You'll leave this curriculum knowing not just what to do, but what you're authorized to do and how to document it.
This is not a course for beginners, and I haven't written it like one. If you're ready to operate at the level where it matters — where the analysis, the architecture, and the judgment are all yours — then this is where you belong. Let's get to work.
— PROF. PETER OLU. OLAYIWOLA, Ph.D.
Start your journey today
Get instant access — learn at your own pace with an AI coach in your corner.
$79/mo
Recurring billing · cancel anytime
Secure checkout · Instant access
- 6 modules, 30 lessons
- AI-adaptive lessons tuned to your level
- Quizzes & checkpoints to lock in progress
- Your own AI learning coach
- Learn on any device, at your pace
- Full access for as long as you're subscribed